Openbyte
Get in Touch →

info@openbyte.co.za
0860 222 111

STABLE • OPEN SOURCE • ICT SOLUTIONS

OPNsense
Firewall Solutions

Enterprise-grade, open-source firewall and routing built on hardened FreeBSD - stateful filtering, VPN, and intrusion prevention in one platform.

What is OPNsense?

OPNsense is a free, open-source firewall and routing platform based on HardenedBSD, a security-focused fork of FreeBSD. It combines the reliability of a mature BSD network stack with a modern, easy-to-use web interface, giving businesses enterprise-grade perimeter security without expensive per-seat licensing.

We deploy and support OPNsense as the firewall layer for South African businesses that need more than a consumer router - stateful packet inspection, built-in VPN endpoints, intrusion detection, and multi-WAN failover, all backed by a large and active open-source community with frequent, audited security updates.

OPNsense pairs naturally with the rest of our stack: it terminates VPN connections for remote and site-to-site access, feeds traffic data into network monitoring, and forms a core part of the hardened perimeter we assess during security assessments. Firewalls are deployed on dedicated hardware or as a virtual appliance under Proxmox, and we run and support them from our Linux and open-source support practice.
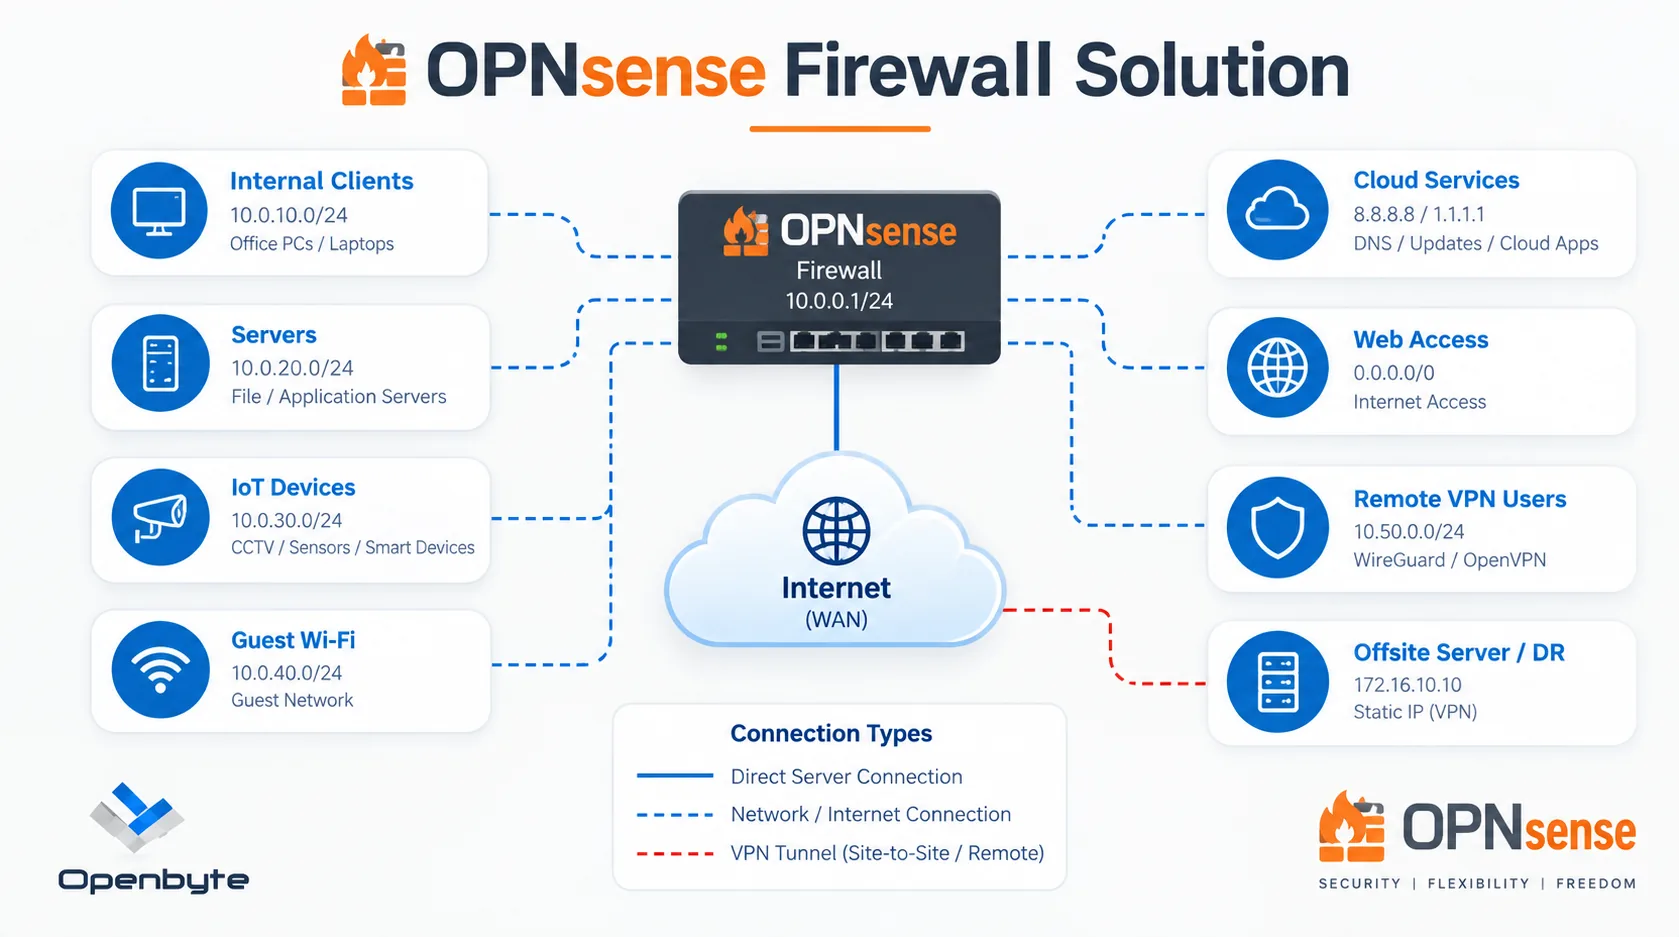
Stateful Firewall IDS/IPS Multi-WAN Failover IPsec / OpenVPN / WireGuard High Availability
OPNsense Firewall Infographic

Click to expand - OPNsense firewall overview

Key Features

OPNsense brings together the core capabilities most businesses need from a firewall appliance, without vendor lock-in or per-feature licence fees.

Stateful Packet Filtering

A mature, high-performance packet filter tracks every connection through the firewall, blocking unsolicited inbound traffic while allowing legitimate return traffic - the foundation of a secure perimeter.

  • Granular rules per interface, zone, or alias
  • Layer 7 application and category filtering
  • Scheduled rules for time-based access

Multi-WAN & Failover

Combine fibre, ADSL, and 4G/5G links for automatic failover or load balancing, keeping your business online even when a primary link drops - common practice given South African connectivity conditions.

  • Gateway monitoring and automatic failover
  • Policy-based routing per link
  • Load balancing across multiple WAN links

Built-In VPN

OPNsense includes IPsec, OpenVPN, and WireGuard endpoints out of the box, letting the firewall itself terminate remote-access and site-to-site VPN tunnels rather than needing separate VPN infrastructure.

  • Site-to-site and road-warrior configurations
  • Certificate-based authentication
  • Integrates with our existing VPN solutions

Intrusion Detection & Prevention

A built-in Suricata-based IDS/IPS engine inspects traffic against continuously updated rule sets, alerting on or actively blocking known attack patterns and malicious traffic before they reach your network.

  • Signature-based and behavioural detection
  • Configurable rule sets (ET Open, custom rules)
  • Feeds alerts into your logging and monitoring

Traffic Shaping & QoS

Prioritise business-critical traffic - VoIP, video conferencing, ERP - over bulk downloads and streaming, so bandwidth-constrained links stay usable during peak hours.

  • Per-application and per-user traffic limits
  • Priority queues for latency-sensitive traffic
  • Fair-queuing for shared internet links

High Availability

Two OPNsense units can be clustered using CARP for stateful failover, so a hardware fault or reboot on one firewall does not take your network offline.

  • Active/passive firewall pairs
  • Synchronised configuration and states
  • Zero-downtime firmware updates

Also Included

  • Web filtering and content proxy (Squid/SquidGuard)
  • Captive portal for guest Wi-Fi networks
  • DHCP, DNS, and dynamic DNS services
  • Plugin ecosystem for extended functionality
  • NetFlow/sFlow export for traffic analysis
  • Two-factor authentication for the web GUI

Why OPNsense Over a Consumer Router or Closed Appliance

OPNsense sits between a consumer router (too limited) and an enterprise firewall appliance (expensive, licence-locked) - open source, auditable, and built for real business networks.

Security & Transparency

  • Built on HardenedBSD with proactive security features
  • Frequent, transparent security releases and changelogs
  • No forced telemetry or vendor cloud dependency
  • Fully auditable open-source codebase
  • Active community and business support ecosystem
  • No artificial feature gating behind paid tiers

Cost & Flexibility

  • No per-user or per-feature licensing fees
  • Runs on commodity hardware or as a VM
  • Scales from small office to multi-site deployments
  • Long-term support without vendor lock-in
  • Plugin system to add features as you need them
  • Straightforward migration path from pfSense

Support & Implementation

We handle the full lifecycle of your OPNsense deployment, from initial design through to ongoing management.

Already running pfSense or a consumer router that's outgrown your business? We handle the migration to OPNsense with minimal downtime.

Frequently Asked Questions

Common questions about OPNsense firewalls from South African businesses.
Is OPNsense really free, or are there hidden licensing costs?
OPNsense itself is free and open-source with no per-feature or per-user licensing. Our fees cover the professional services - design, installation, configuration, and ongoing support - plus any hardware you choose to purchase through us.
How is OPNsense different from pfSense?
OPNsense is a fork of pfSense/m0n0wall built on HardenedBSD, with a stronger focus on code auditing, a modern web GUI, and more frequent security releases. We support both, but generally recommend OPNsense for new deployments due to its development pace and security posture.
Can OPNsense replace our existing VPN setup?
Yes. OPNsense includes IPsec, OpenVPN, and WireGuard endpoints, so it can terminate remote-access and site-to-site VPNs directly on the firewall. We can consolidate your existing VPN solution onto the firewall or keep them separate, depending on your architecture.
Do you support high-availability firewall pairs?
Yes. We configure active/passive OPNsense pairs using CARP for synchronised state and configuration failover, so a hardware fault or reboot on one unit does not interrupt connectivity.
Linux Docker GCP Ubuntu Nextcloud Wazuh BareOS Zabbix OPNsense Claude Linux Docker GCP Ubuntu Nextcloud Wazuh BareOS Zabbix OPNsense Claude